Skip to content

i-doit Suite+ ISMS

Integrated ISMS for certifications with CMDB as data foundation

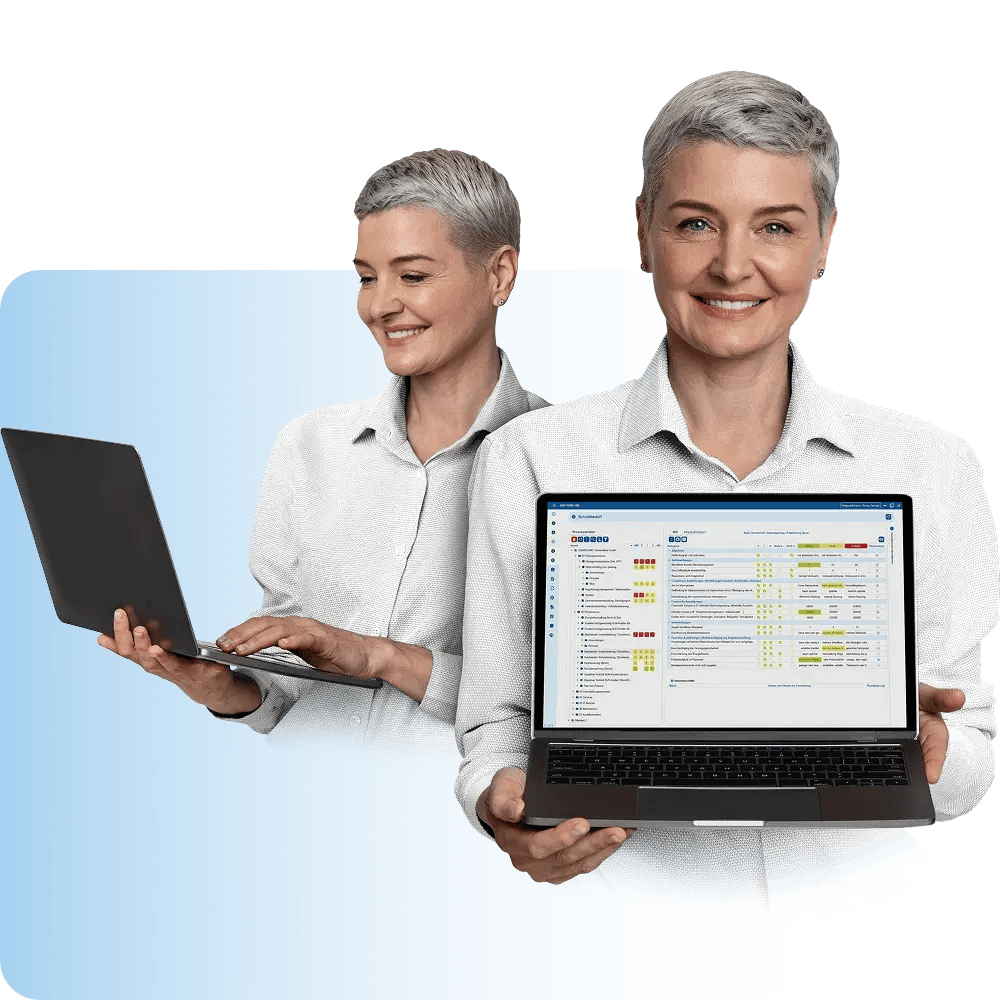
Effectively implement ISO 27001, NIS-2, and numerous other certifications — thanks to CMDB data foundation and a networked GRC ecosystem, you create transparency, automate processes, and sustainably strengthen your information security. Available in the cloud or on- premises.

rating-stars-transparent-white 4.7/5 on Capterra | 2.000+ satisfied customers
i-doit-inditor-header

Try i-doit Suite+ ISMS free for 30 days now

icon-it-documentation-in-team-dk
2.000+ customers
icon-api-dk
No payment details required
icon-link-dk
Support included
icon-digital-contract-management-dk
Full feature set
icon-it-security-dk
GDPR compliant

Multiple certifications in one solution

Enjoy the freedom to integrate a variety of requirement catalogs into your instance

grcsuiteplus_KAtalog
icon-it-documentation-in-team-lt ISO certifications
Numerous ISO catalogs are already available in i-doit Suite+ ISMS and can be used immediately when needed, e.g.: ISO 27001, ISO 27002, ISO 9001, ISO 27019  
icon-link-lt TISAX®/VDA-ISA

Certification for security requirements for companies within the automotive supply chain

 
icon-digital-contract-management-lt NIS-2

Support for NIS-2 implementation incl. exclusive NIS-2 checklist

 
icon-it-security-lt Additional certifications

Additional certifications possible such as: B3S (Industry-specific security standard for clinics and hospitals) and coming soon VAIT, BAIT, VdS 10000 and many more
 

Your integrated ISMS that links risks, assets, and evidence

Unique information security management system in the cloud or on-premises

grcsuiteplus_BIA
icon-link-dk Asset map visualization
Visualization of even highly complex IT infrastructures in a simplified representation via the asset map  
icon-digital-contract-management-dk Protection requirements assessment
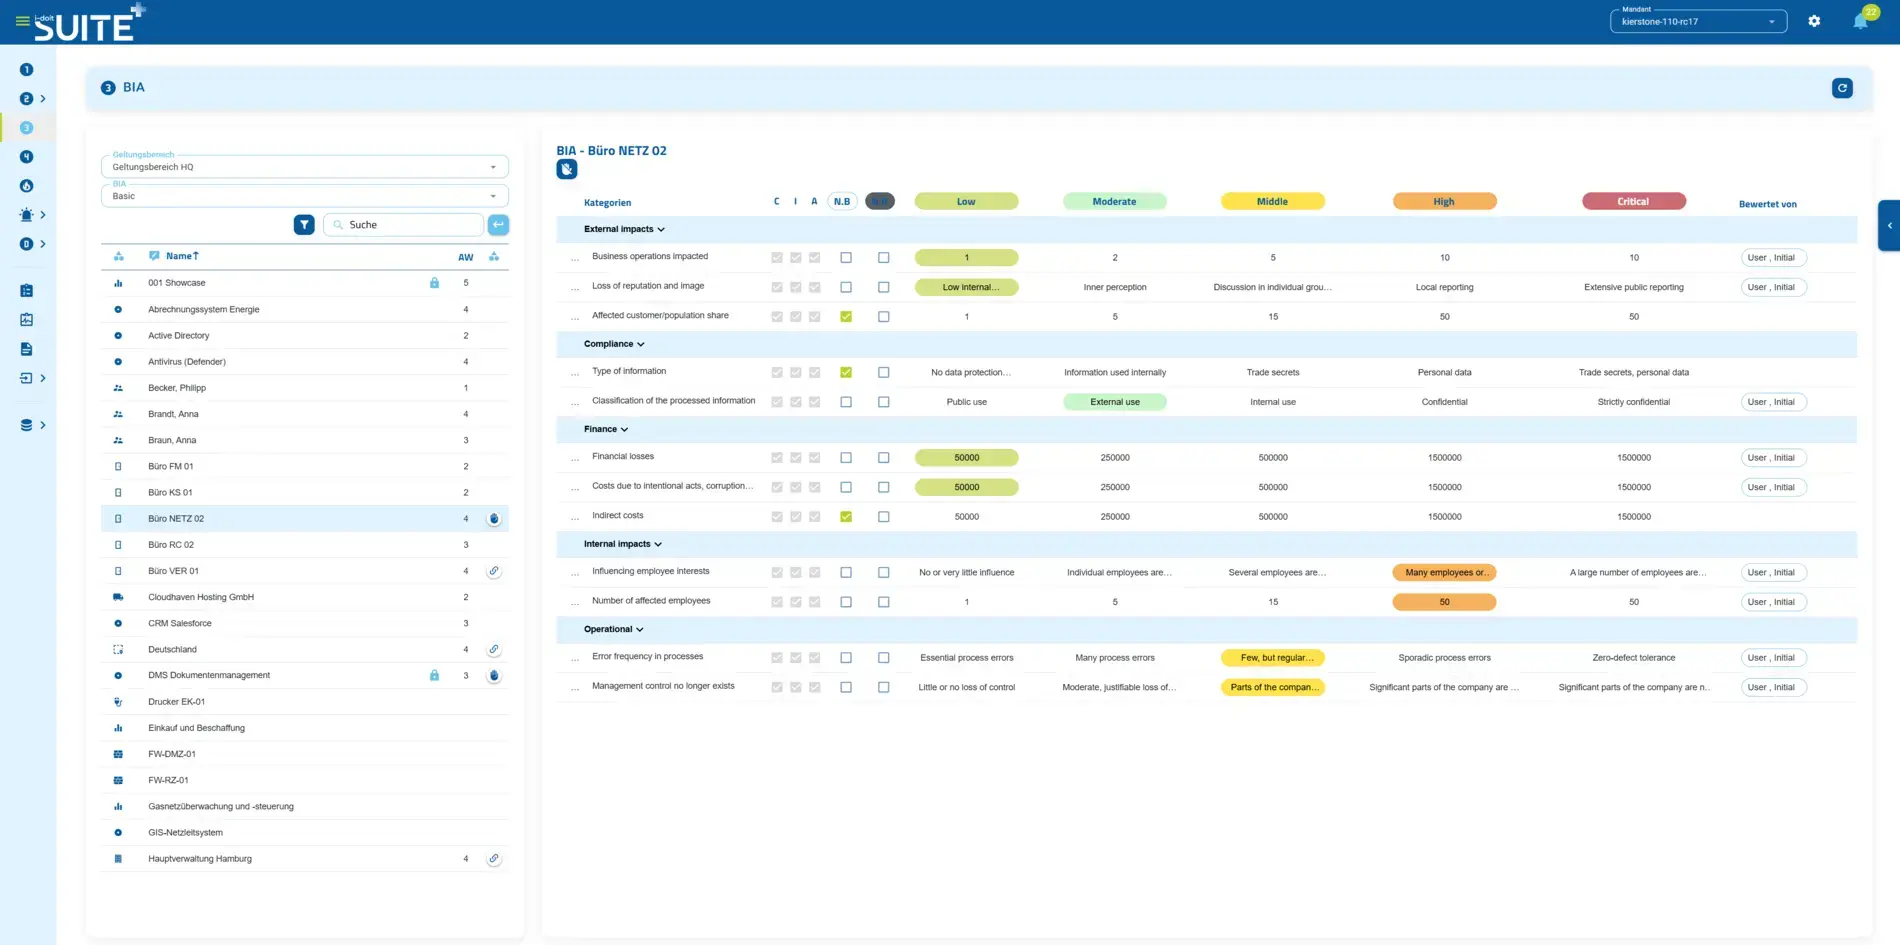
Conducting protection requirements analysis at asset & process level  
icon-it-documentation-in-team-dk Risk & measure management
Flexible risk management - protection requirements are automatically inherited, risks assessed, and measures derived. For ISMS, BCM, and data protection on a shared data foundation  
icon-api-dk DMS for documents, audits & evidence

The document management system (DMS) with versioning and approval processes provides audit-proof evidence for inspections, audits, and compliance reporting
 
icon-it-security-dk Audit management
You centrally manage audits, plan inspections, and document results – including automatically generated audit reports for your evidence management.  

CMDB as data foundation

The i-doit GRC Suite+ brings your CMDB right with it – for GRC processes on a reliable data foundation.

grcsuiteplus_Assetmanagemetn2
icon-it-documentation-in-team-lt Complete transparency
All IT assets, dependencies, and relationships at a glance – the foundation for informed risk management decisions.  
icon-api-lt Always current inventory
Automated inventory management ensures your asset data never becomes outdated – manual Excel lists are a thing of the past.  
icon-link-lt Make dependencies visible
Relationships between systems, applications, and processes become traceable – so impacts of outages or risks can be realistically assessed.  
icon-digital-contract-management-lt Well-founded decision foundation
A reliable data foundation reduces poor decisions and accelerates audits, inspections, and compliance reporting.  

Your solution for requirement catalogs

Benefits of your ISMS solution

i-doit Suite+ ISMS feature overview

The next-gen emergency platform in the cloud & on-premises

i-doit Suite+ ISMS

Administration
idoit-check-mark
Master data
idoit-check-mark
Reports
idoit-check-mark
Asset management
idoit-check-mark
Document management
idoit-check-mark
Risk management
idoit-check-mark
Measures management
idoit-check-mark
Purchase lisence
Optional
Multitenant
idoit-check-mark
Role and permissions
idoit-check-mark
Shared database with ISMS, BCM & IT contingency planning
idoit-check-mark
Cloud or on-premises, your choice
idoit-check-mark
Template and document control (coming soon)
idoit-check-mark
Dashboard (coming soon)
idoit-check-mark
Objectives management (coming soon)
Optional
Supplier management (coming soon)
Optional
Protection needs analysis (BIA)
idoit-check-mark
Security incident management
idoit-check-mark
NIS2 checklist
idoit-check-mark
Requirement catalogs
Optional
Audit management (coming soon)
idoit-check-mark

Use cases

Use cases relating to ISMS, risk and compliance management

Audit management
Audit management

You control audits centrally, plan audits, document results and automatically generate audit reports.

View use case

Document management
Document management

You can manage documents in an audit-proof manner, version and edit them directly in the tool and use templates and import functions.

View use case

GAP analysis
GAP analysis

i-doit supports GAP analyses according to standards such as ISO 27001, ISO 9001 or NIS2, including maturity level assessment, responsibilities and document assignment.

View use case

Supplier management
Supplier management

You evaluate and manage suppliers centrally, document contracts and maintain contact details and replacement suppliers.

View use cases

Action management
Action management

You derive measures, distribute tasks, track deadlines and receive automatic notifications by e-mail.

View use case

Security incident management

You document and evaluate security incidents in accordance with ISO and NIS2, assign affected assets and centrally derive measures.
View use case

contact-cta-bg-dark-bottom-align

Book your personal live demo

Our i-doit team is happy to take the time to personally advise you on your use case.
i-doit Suite+ ISMS overview

Your ISMS that guides you step by step through your certification

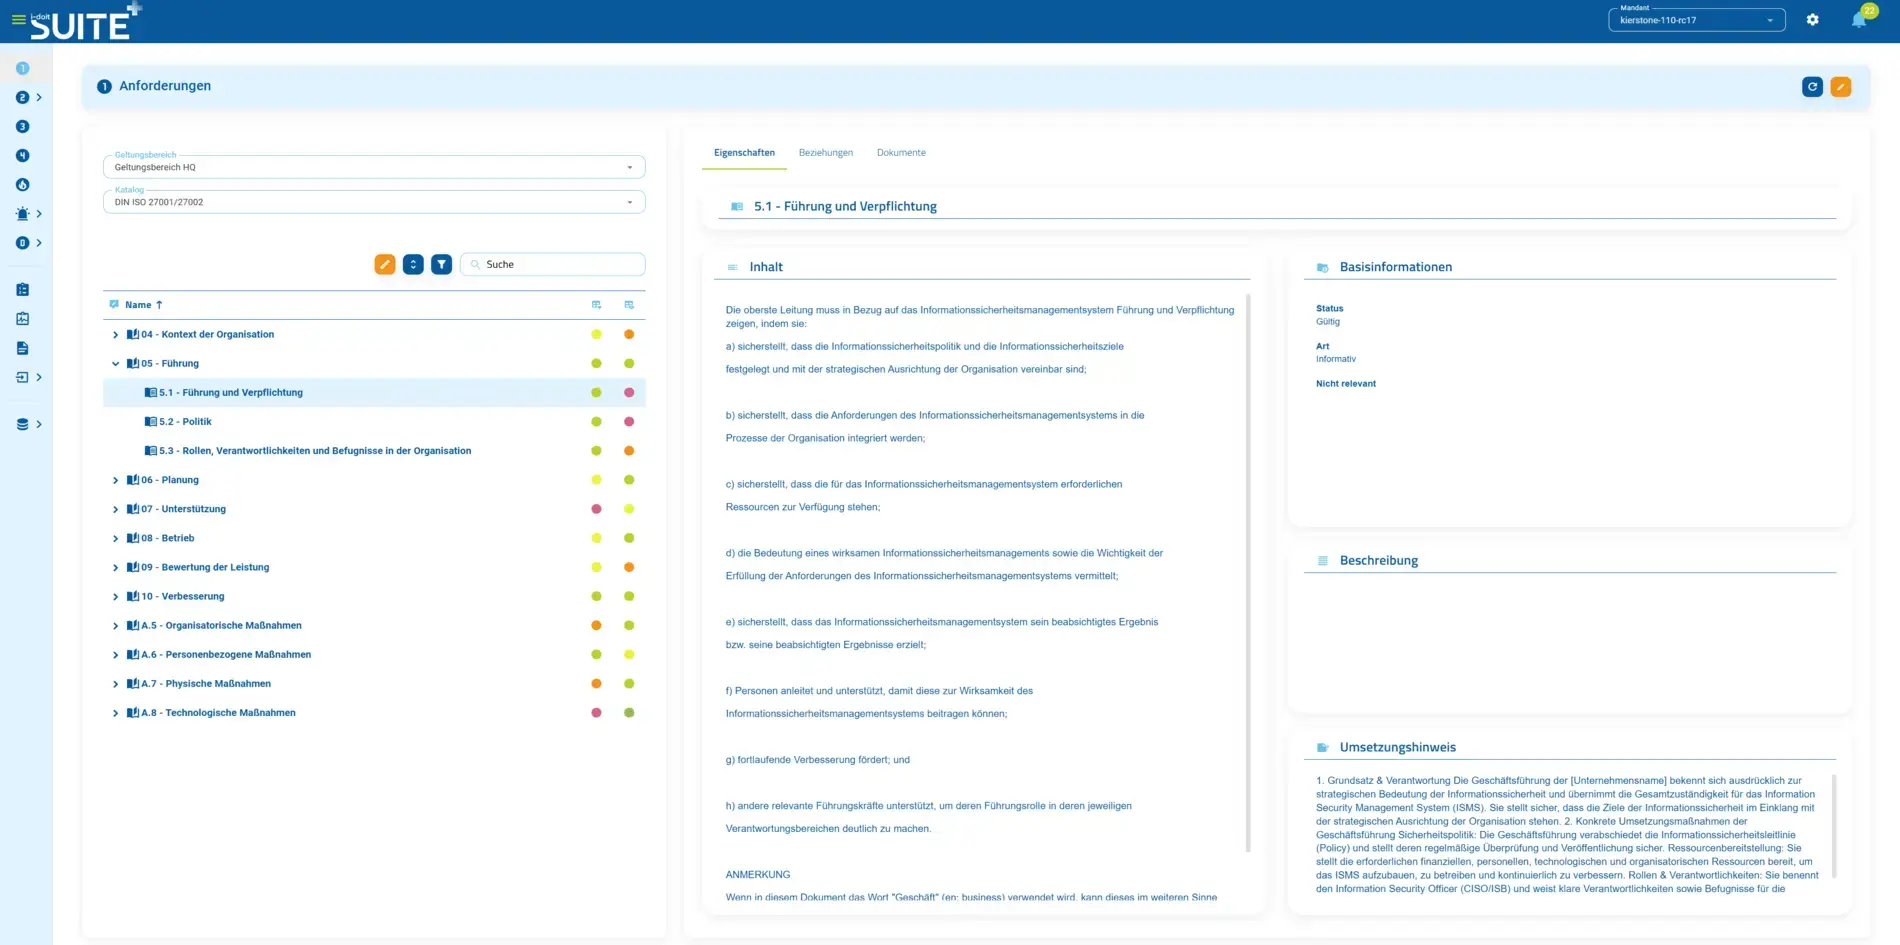
1. Requirement catalog

Mapping of the requirements of the ISO/IEC 27001 catalog linked to the scope. The requirements and measures in i-doit Suite+ are supplemented with implementation guidance and assistance. ISO/IEC 27002 is automatically linked.

Define responsibilities, implementation status, and measures for individual requirements. Link relevant policies (e.g., compliance) and documents for the requirements and add implementation guidance.


grcsuiteplus_KAtalog

2. Asset management

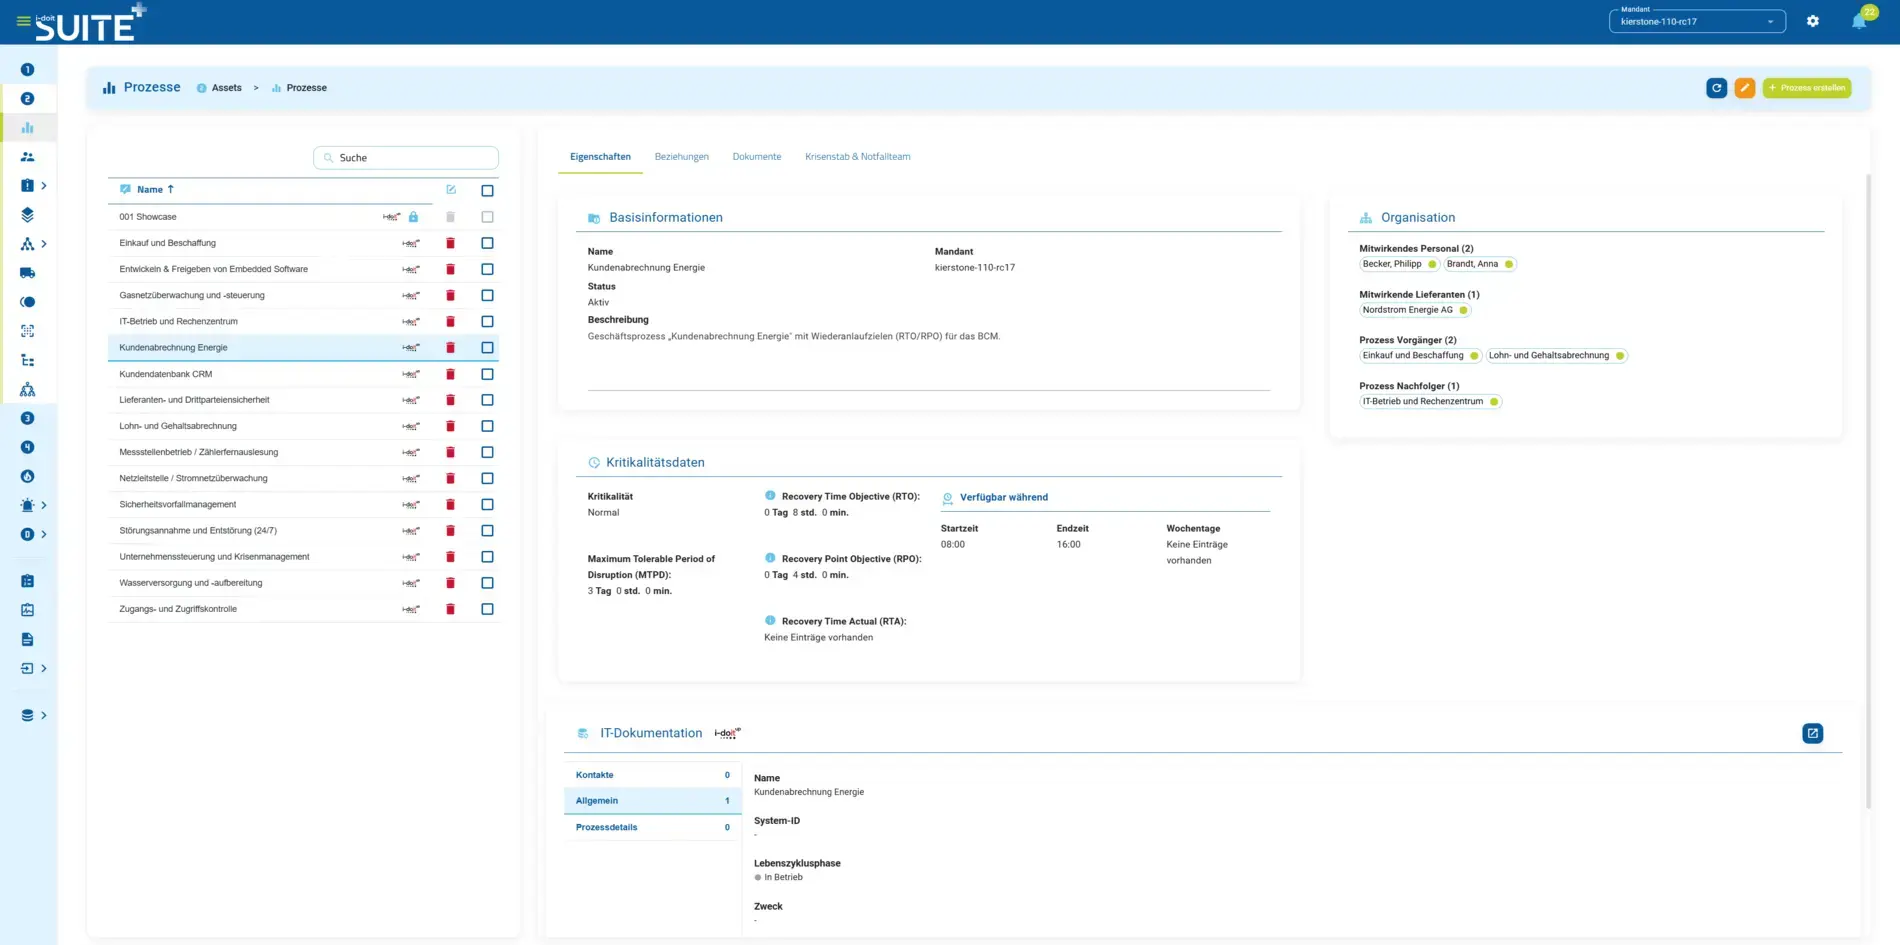
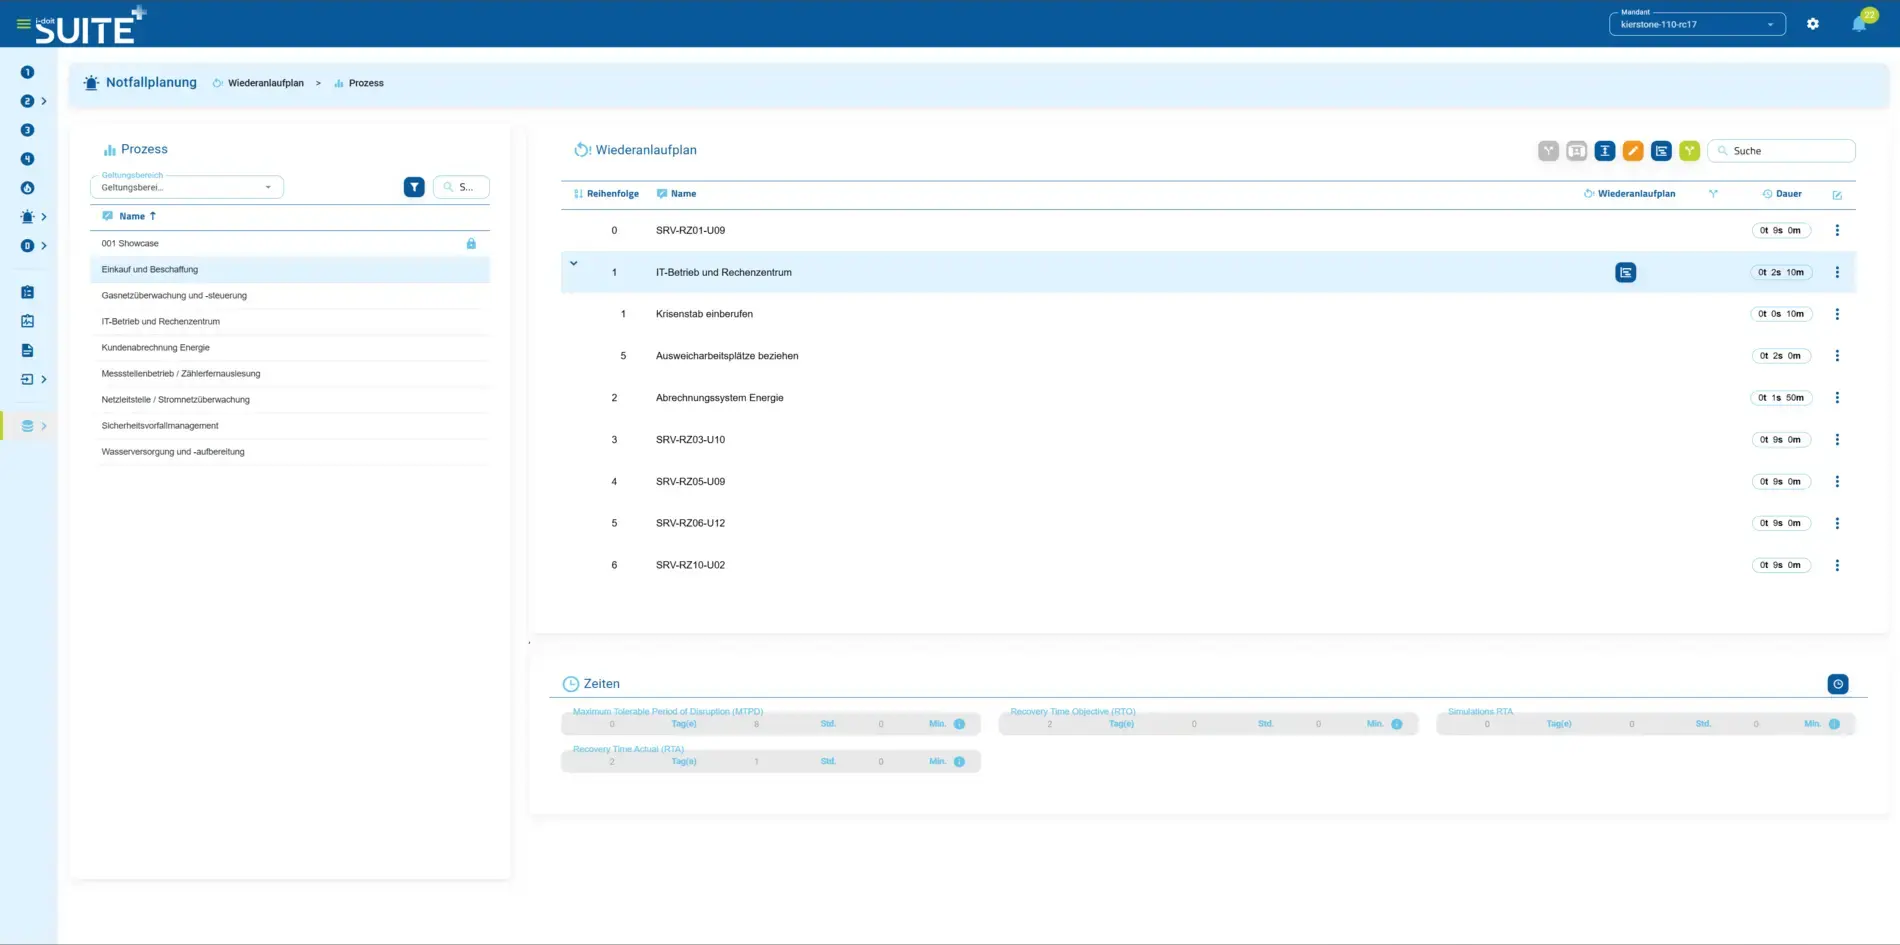
With asset management in i-doit Suite+ ISMS, you centrally manage processes, personnel, and IT infrastructure. Included ISO-compliant standard processes can be extended and imported.

Asset trees, groups, and dependencies support risk assessments in risk management. Existing inventory and IT solutions, vendors, and organizational units can be easily integrated. For maximum transparency in complex enterprises.

grcsuiteplus_Wiederanlauf Prozess BCMNotfall

3. Protection requirements assessment

Protection requirements determine how important a process is for the functioning of all other processes in an organization. You can make this determination in our software through a customizable Business Impact Analysis (BIA). This can be individually adapted to your organization's circumstances and structures.


grcsuiteplus_BIA

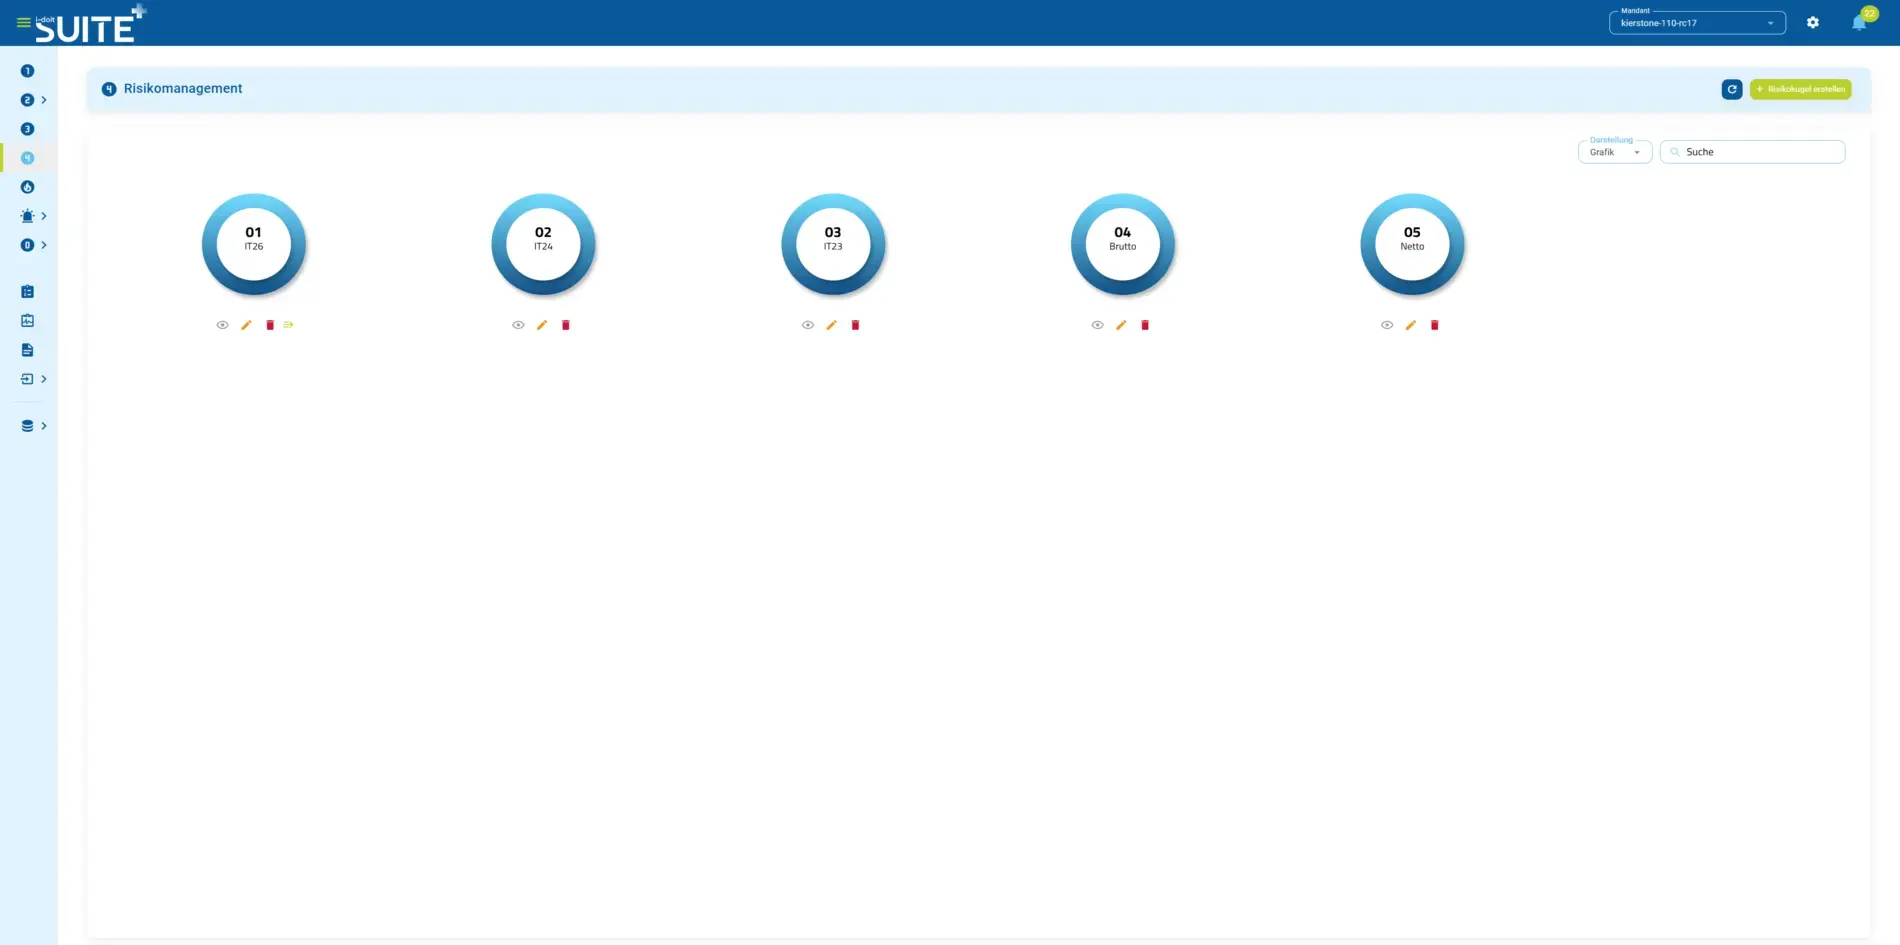
4. Risk assessment

In risk assessment, you determine how high the probability of a risk occurring in a given scenario is. You assess the probability that these threats will impact your organization and what consequences this impact would likely have for your organization.

grcsuiteplus_Risikokugeln

5. Audit management

With audit management, you optimally prepare for certification, e.g., according to ISO/IEC 27001. You have the ability to plan audits, manage them, and check current implementation status. Match already implemented security measures against ISO standard requirements to identify the achieved security level and highlight improvement opportunities.

grcsuiteplus_Auditmanagement

Industries

View all solutions for your industry

What is i-doit Suite+ ISMS?

What is an ISMS and why do I need it?

An Information Security Management System (ISMS) is a framework for managing information security across an organization. It defines policies, processes, and controls to protect confidentiality, integrity, and availability of information assets. You need an ISMS because regulatory requirements, industry standards, and business risk management all demand demonstrable, systematic information security. i-doit Suite+ ISMS helps you implement, maintain, and continuously improve your ISMS efficiently.
 

Which standards and norms does the ISMS tool support?

i-doit Suite+ ISMS supports multiple international standards and regulatory frameworks including:

  • ISO 27001 (Information Security Management)


  • ISO 27002 (Information Security Controls)


  • NIS2 (Network and Information Security Directive 2)


  • TISAX (Trusted Information Security Assessment Exchange)


  • BSI C5 and BSI IT-Grundschutz


  • GDPR (integrated with i-doit Suite+ Data Protection)


  • Industry-specific compliance frameworks

What does NIS2 mean and who does it apply to?

NIS2 (Network and Information Security Directive 2) is a European Union regulation that strengthens information security and incident response requirements. It applies to operators of essential services (critical infrastructure) and important digital service providers in sectors like energy, transportation, healthcare, finance, and digital infrastructure. Even if you're not directly regulated, customers or partners subject to NIS2 may require your compliance.

How does the ISMS module help me implement NIS2?

i-doit Suite+ ISMS helps implement NIS2 by:

  • Providing pre-configured NIS2 requirement catalogs matching the directive's demands


  • Enabling systematic mapping of organizational processes to specific NIS2 controls


  • Automating risk assessment aligned with NIS2 risk management requirements


  •  Tracking implementation of security measures linked to NIS2 obligations


  • Generating compliance documentation and audit evidence for authorities


  • Integrating incident management to meet NIS2 breach notification requirements

What is the difference between ISO 27001 and NIS2?

ISO 27001 is a voluntary international standard for implementing a comprehensive information security management system applicable to any organization. NIS2 is a mandatory EU regulation targeting specific sectors (critical infrastructure and important digital service providers) with minimum security requirements. ISO 27001 is broader and more flexible; NIS2 is sector-specific and legally binding. Organizations can be subject to both—ISO 27001 provides the framework, NIS2 defines minimum requirements for regulated entities.


Can I use the solutions in combination?

Yes. i-doit Suite+ ISMS can be deployed as a standalone product or combined with other solutions in the i-doit GRC Suite+ including Emergency Planning, BCM, and Data Protection. A unified approach provides shared data across systems, eliminates duplicate information entry, and ensures consistent security and compliance management across your entire organization.

What benefits does using the software provide?

Key benefits include:

  • Systematic, auditable information security management aligned with standards


  • Reduced manual effort through automation of common ISMS processes


  • Centralized documentation of security policies, controls, and compliance status


  • Integrated risk and incident management linked to remediation measures


  • Real-time compliance status and audit-ready reporting


  • Improved visibility into information assets and their security posture


  • Faster response to regulatory audits and compliance assessments

How do I get started with implementation?

Getting started is straightforward: Begin with a 30-day free trial that includes a 30-minute setup appointment with our i-doit team. They help you configure your test environment and identify your most pressing security and compliance requirements. You can explore pre-configured requirement catalogs for your relevant standards (ISO 27001, NIS2, etc.) and map them to your organization's existing processes. For a personalized walkthrough, book a demo with our experts.

Can I implement ISMS, emergency planning, and data protection together?

Yes. The i-doit GRC Suite+ is designed to enable integrated governance, risk, and compliance management across ISMS, Emergency Planning, Data Protection, and BCM in a single solution. This unified approach provides:

  • Shared asset and process information across all modules


  • Consistent risk assessment across security, data protection, and business continuity domains


  • Unified incident and breach notification management


  • Comprehensive compliance reporting across all frameworks

What CMDB integration is available?

i-doit Suite+ ISMS has native integration with the i-doit up CMDB (Configuration Management Database), enabling you to seamlessly connect information security management with your actual IT infrastructure. This integration allows you to:

  • Link security controls to the IT systems they protect


  • Assess impact of security incidents on your IT environment


  • Maintain accurate asset inventory for risk assessment


  • Synchronize data between ISMS and CMDB without manual re-entry